Category Archives: PLAYERS

Opening the Black Box of America’s Propaganda Machine – Prepare for Change

National Security Agency whistleblower Edward Snowden and WikiLeaks founder Julian Assange have doubled down recently on the games being played in cyberspace by America‘s cyber-warriors.

Snowden suggests that many of NSA’s most damaging malware programs are now in the hands of America’s opponents, thanks to enterprising foreign counter-intelligence hackers known as the Shadow Brokers. there will be more hacked bombshells to drop on Team Clinton, courtesy of weak security in Democratic National Committee and Clinton campaign computer systems.

We have entered a new phase of cyber-warfare, one in which America’s (and Israel’s) most damaging computer hacking and disruption programs are available to anyone willing to pay in Bitcoins on the cyber-black market. The Democratic Party’s leaked emails, coupled with the leaked State Department cables, has Hillary Clinton in an outrage.

These disclosures, along with the Snowden disclosures that illustrate how America spies on friend and foe, have opened the Black Box of America’s propaganda machine.

Continue reading Opening the Black Box of America’s Propaganda Machine – Prepare for Change →

The N.S.A. Leak Is Real, Snowden Documents Confirm

MON, 8/22/2016 BY SAM BIDDLE

 On Monday, a hacking group calling itself the “ShadowBrokers” announced an auction for what it claimed were “cyber weapons” made by the NSA. Based on never-before-published documents provided by the whistleblower Edward Snowden, The Intercept can confirm that the arsenal contains authentic NSA software, part of a powerful constellation of tools used to covertly infect computers worldwide.

The provenance of the code has been a matter of heated debate this week among cybersecurity experts, and while it remains unclear how the software leaked, one thing is now beyond speculation: The malware is covered with the NSA’s virtual fingerprints and clearly originates from the agency.

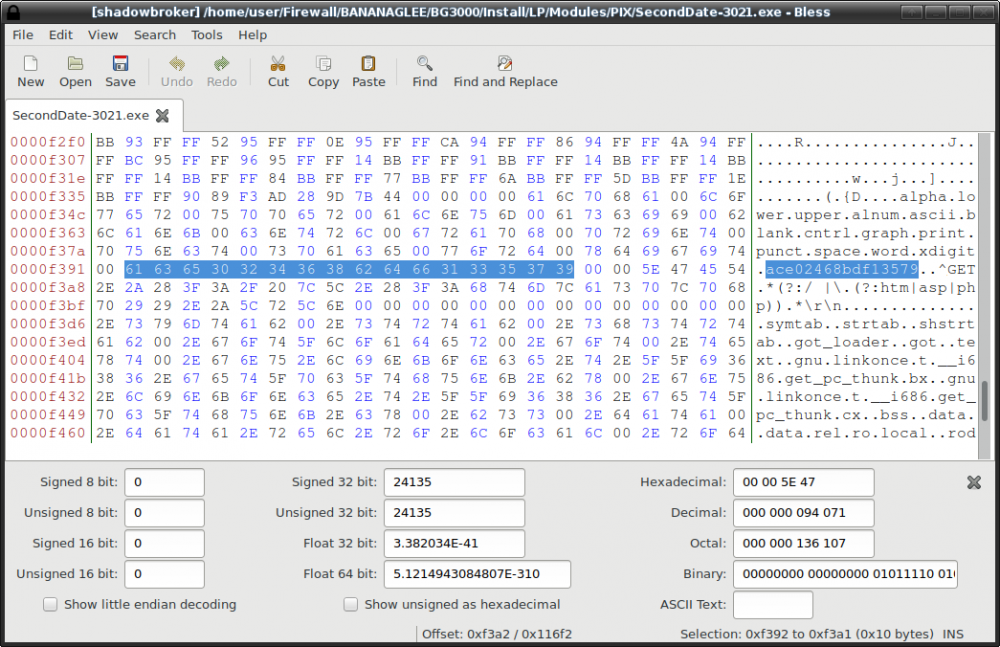
The evidence that ties the ShadowBrokers dump to the NSA comes in an agency manual for implanting malware, classified top secret, provided by Snowden, and not previously available to the public. The draft manual instructs NSA operators to track their use of one malware program using a specific 16-character string, “ace02468bdf13579.” That exact same string appears throughout the ShadowBrokers leak in code associated with the same program, SECONDDATE.

SECONDDATE plays a specialized role inside a complex global system built by the U.S. government to infect and monitor what one document estimated to be millions of computers around the world. Its release by ShadowBrokers, alongside dozens of other malicious tools, marks the first time any full copies of the NSA’s offensive software have been available to the public, providing a glimpse at how an elaborate system outlined in the Snowden documents looks when deployed in the real world, as well as concrete evidence that NSA hackers don’t always have the last word when it comes to computer exploitation.

But malicious software of this sophistication doesn’t just pose a threat to foreign governments, Johns Hopkins University cryptographer Matthew Green told The Intercept:

The danger of these exploits is that they can be used to target anyone who is using a vulnerable router. This is the equivalent of leaving lockpicking tools lying around a high school cafeteria. It’s worse, in fact, because many of these exploits are not available through any other means, so they’re just now coming to the attention of the firewall and router manufacturers that need to fix them, as well as the customers that are vulnerable. So the risk is twofold: first, that the person or persons who stole this information might have used them against us. If this is indeed Russia, then one assumes that they probably have their own exploits, but there’s no need to give them any more. And now that the exploits have been released, we run the risk that ordinary criminals will use them against corporate targets.

The NSA did not respond to questions concerning ShadowBrokers, the Snowden documents, or its malware.

A MEMORABLE SECONDDATE

The offensive tools released by ShadowBrokers are organized under a litany of code names such as POLARSNEEZE and ELIGIBLE BOMBSHELL, and their exact purpose is still being assessed. But we do know more about one of the weapons: SECONDDATE.

SECONDDATE is a tool designed to intercept web requests and redirect browsers on target computers to an NSA web server. That server, in turn, is designed to infect them with malware. SECONDDATE’s existence was first reported by The Intercept in 2014, as part of a look at a global computer exploitation effort code-named TURBINE. The malware server, known as FOXACID, has also been described in previously released Snowden documents.

Other documents released by The Intercept today not only tie SECONDDATE to the ShadowBrokers leak but also provide new detail on how it fits into the NSA’s broader surveillance and infection network. They also show how SECONDDATE has been used, including to spy on Pakistan and a computer system in Lebanon.

The top-secret manual that authenticates the SECONDDATE found in the wild as the same one used within the NSA is a 31-page document titled “FOXACID SOP for Operational Management” and marked as a draft. It dates to no earlier than 2010. A section within the manual describes administrative tools for tracking how victims are funneled into FOXACID, including a set of tags used to catalogue servers. When such a tag is created in relation to a SECONDDATE-related infection, the document says, a certain distinctive identifier must be used.

The same SECONDDATE MSGID string appears in 14 different files throughout the ShadowBrokers leak, including in a file titled SecondDate-3021.exe. Viewed through a code-editing program (screenshot below), the NSA’s secret number can be found hiding in plain sight.

All told, throughout many of the folders contained in the ShadowBrokers’ package (screenshot below), there are 47 files with SECONDDATE-related names, including different versions of the raw code required to execute a SECONDDATE attack, instructions for how to use it, and other related files.

After viewing the code, Green told The Intercept the MSGID string’s occurrence in both an NSA training document and this week’s leak is “unlikely to be a coincidence.” Computer security researcher Matt Suiche, founder of UAE-based cybersecurity startup Comae Technologies, who has been particularly vocal in his analysis of the ShadowBrokers this week, told The Intercept “there is no way” the MSGID string’s appearance in both places is a coincidence.

WHERE SECONDDATE FITS IN

This overview jibes with previously unpublished classified files provided by Snowden that illustrate how SECONDDATE is a component of BADDECISION, a broader NSA infiltration tool. SECONDDATE helps the NSA pull off a “man in the middle” attack against users on a wireless network, tricking them into thinking they’re talking to a safe website when in reality they’ve been sent a malicious payload from an NSA server.

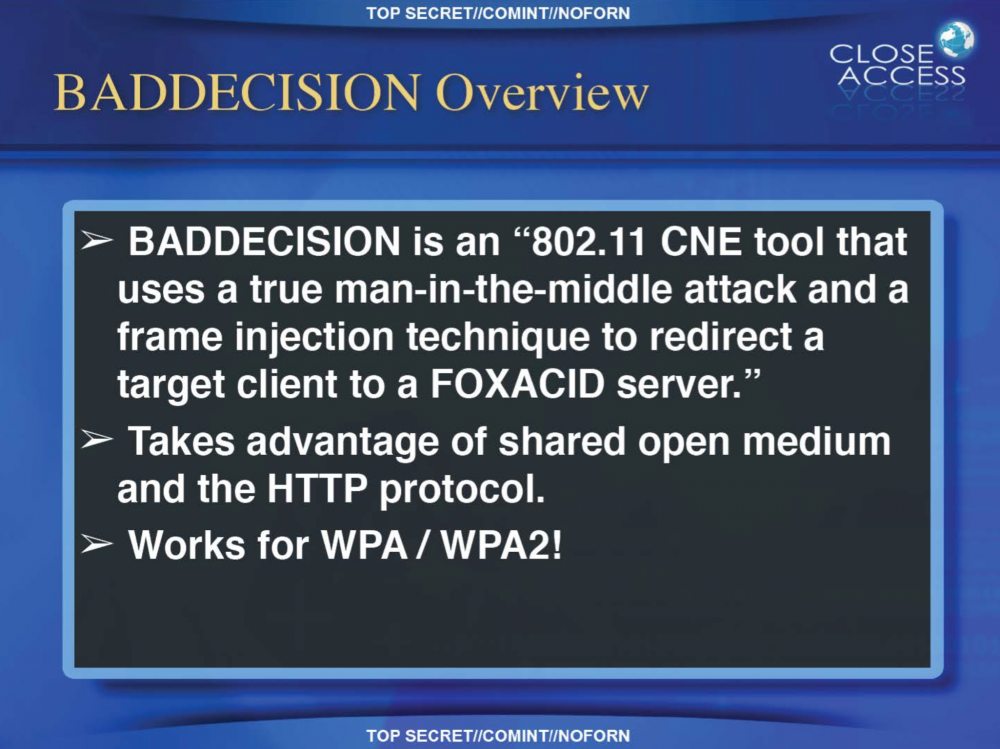
According to one December 2010 PowerPoint presentation titled “Introduction to BADDECISION,” that tool is also designed to send users of a wireless network, sometimes referred to as an 802.11 network, to FOXACID malware servers. Or, as the presentation puts it, BADDECISION is an “802.11 CNE [computer network exploitation] tool that uses a true man-in-the-middle attack and a frame injection technique to redirect a target client to a FOXACID server.” As another top-secret slide puts it, the attack homes in on “the greatest vulnerability to your computer: your web browser.”

One slide points out that the attack works on users with an encrypted wireless connection to the internet.

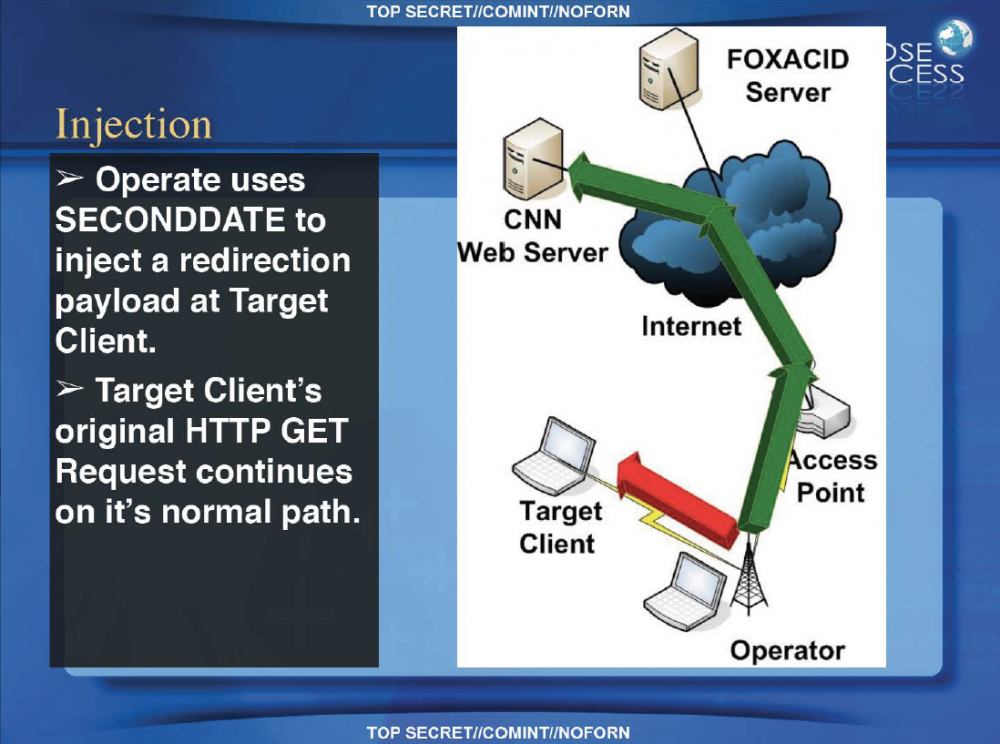
That trick, it seems, often involves BADDECISION and SECONDDATE, with the latter described as a “component” for the former. A series of diagrams in the “Introduction to BADDECISION” presentation show how an NSA operator “uses SECONDDATE to inject a redirection payload at [a] Target Client,” invisibly hijacking a user’s web browser as the user attempts to visit a benign website (in the example given, it’s CNN.com). Executed correctly, the file explains, a “Target Client continues normal webpage browsing, completely unaware,” lands on a malware-filled NSA server, and becomes infected with as much of that malware as possible — or as the presentation puts it, the user will be left “WHACKED!” In the other top-secret presentations, it’s put plainly: “How do we redirect the target to the FOXACID server without being noticed”? Simple: “Use NIGHTSTAND or BADDECISION.”

The sheer number of interlocking tools available to crack a computer is dizzying. In the FOXACID manual, government hackers are told an NSA hacker ought to be familiar with using SECONDDATE along with similar man-in-the-middle wi-fi attacks code-named MAGIC SQUIRREL and MAGICBEAN. A top-secret presentation on FOXACID lists further ways to redirect targets to the malware server system.

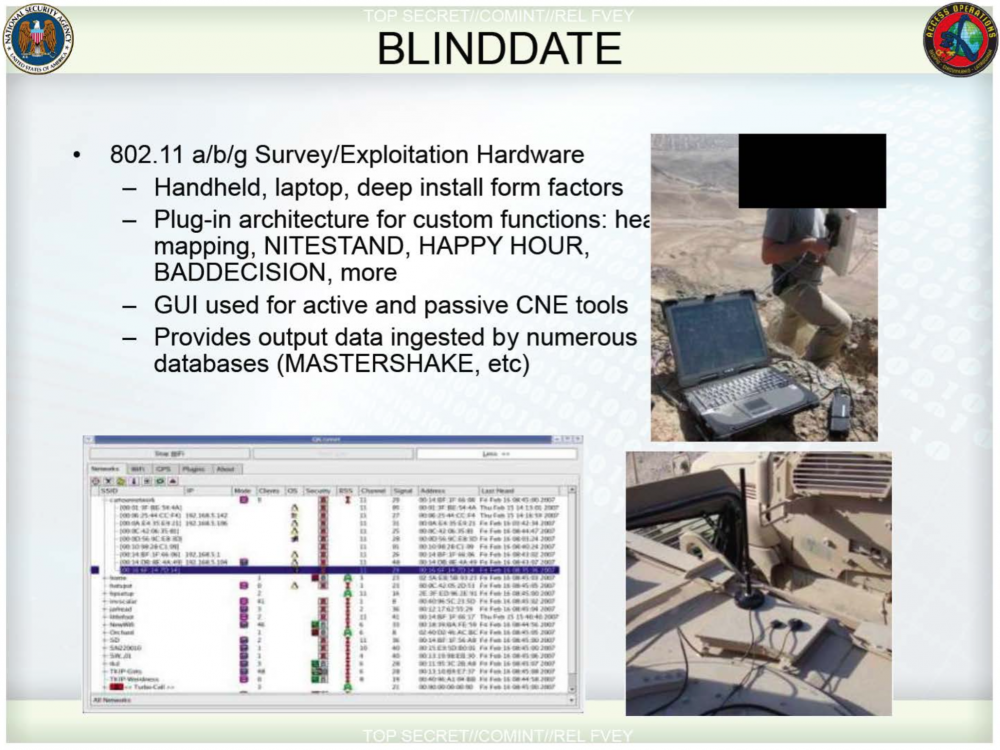
To position themselves within range of a vulnerable wireless network, NSA operators can use a mobile antenna system running software code-named BLINDDATE, depicted in the field in what appears to be Kabul. The software can even be attached to a drone. BLINDDATE in turn can run BADDECISION, which allows for a SECONDDATE attack.

Elsewhere in these files, there are at least two documented cases of SECONDDATE being used to successfully infect computers overseas: An April 2013 presentation boasts of successful attacks against computer systems in both Pakistan and Lebanon. In the first, NSA hackers used SECONDDATE to breach “targets in Pakistan’s National Telecommunications Corporation’s (NTC) VIP Division,” which contained documents pertaining to “the backbone of Pakistan’s Green Line communications network” used by “civilian and military leadership.”

In the latter, the NSA used SECONDDATE to pull off a man-in-the-middle attack in Lebanon “for the first time ever,” infecting a Lebanese ISP to extract “100+ MB of Hizballah Unit 1800 data,” a special subset of the terrorist group dedicated to aiding Palestinian militants.

SECONDDATE is just one method that the NSA uses to get its target’s browser pointed at a FOXACID server. Other methods include sending spam that attempts to exploit bugs in popular web-based email providers or entices targets to click on malicious links that lead to a FOXACID server. One document, a newsletter for the NSA’s Special Source Operations division, describes how NSA software other than SECONDDATE was used to repeatedly direct targets in Pakistan to FOXACID malware web servers, eventually infecting the targets’ computers.

A POTENTIALLY MUNDANE HACK

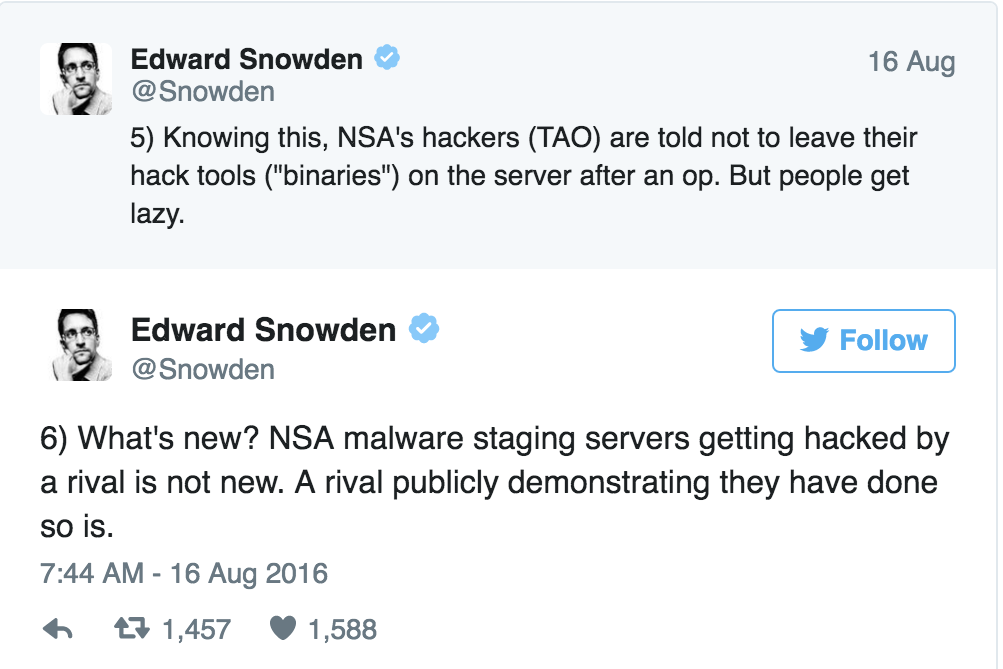
Snowden, who worked for NSA contractors Dell and Booz Allen Hamilton, has offered some context and a relatively mundane possible explanation for the leak: that the NSA headquarters was not hacked, but rather one of the computers the agency uses to plan and execute attacks was compromised. In a series of tweets, he pointed out that the NSA often lurks on systems that are supposed to be controlled by others, and it’s possible someone at the agency took control of a server and failed to clean up after themselves. A regime, hacker group, or intelligence agency could have seized the files and the opportunity to embarrass the agency.
Source: The N.S.A. Leak Is Real, Snowden Documents Confirm

FBI Uncovers Over 15,000 More Emails In Clinton Probe | Zero Hedge

Tyler Durden's picture

Updating our earlier note, it appears The State Department’s stalling has been disallowed… (as Bloomberg reports)

A judge ordered the State Department to expedite its review of almost 15,000 previously undisclosed documents recovered by the FBI from Hillary Clinton’s private e-mail servers.

U.S. District James Boasberg on Monday ordered the State Department to process those recovered records by Sept. 22 and report back to him that day. He didn’t set a schedule for public release. The department raised the possibility of a phased release starting Oct. 14, which left open how many would be disclosed before the Nov. 8 presidential election.

As we detailed earlier, in yet another incident pointing to Hillary’s ‘above the law’ persistent lies, WaPo reports The FBI’s year-long investigation of Hillary Clinton’s private email server uncovered tens of thousands more documents from her time as secretary of state that were not previously disclosed by her attorneys. Worse still, as Judicial Watch details, “it looks like the State Department is trying to slow roll the release of the records.”

Continue reading FBI Uncovers Over 15,000 More Emails In Clinton Probe | Zero Hedge →

Kazarian Mafia In Total Panic – DR WILLIAM MOUNT

VIDEO: Kazarian Mafia In Total Panic – YouTube

The Unholy Alliance (NWO, Cabal, Unholy Alliance) is in total panic mode at this moment in time

Last night, while most of us were asleep, the orders were given to initiate Operation Pincer: The invasion of Russia by forces of the German, Polish and French Governments – with the United States to follow and “Save The Day” and “Re-establish Peace” in Russia – 1 Million People Praying

Nobody invaded anybody.

The artillery was silent and the US Air Force stood down.

Of course – they never factored in the response from Belarus either – which has a fierce military. The though of an Invasion there by Germany as ordered by Hitler’s Daughter Angela Merkel brings back memories that should never be remembered – destruction, death camps….

Continue reading Kazarian Mafia In Total Panic – DR WILLIAM MOUNT →

The main factions in the battle for the planet earth and their current status – Weekly geo-political news and analysis Message from Benjamin Fulford

August 22, 2016 by benjamin

The ongoing battle for control of the financial system, and thus control over the process of deciding what we as a species will be doing in the future, is reaching a climax. For this reason, this might be a good time to look at who the major players are and what their position is.

First of all, let us look at the Khazarian/Nazi faction that took over control of the Europe, Japan and the United States following the September 11, 2001 false flag attack in New York. This faction is led by George Bush Sr., David Rockefeller and their lackeys. Their plan was to reduce the world’s population by 90% through starvation, disease and war. Ample proof of this has been provided to various police, military and intelligence agencies around the world. Since the Nazi takeover of the United States was completed with the election stolen by George Bush Jr. in the year 2000 the government of the United States has tried to murder us through the release of bio-weapons including SARS, Bird Flu, Ebola etc

Continue reading The main factions in the battle for the planet earth and their current status – Weekly geo-political news and analysis Message from Benjamin Fulford →

Putin “Erupts” Over Million Dollar “Spy Payments” To Hillary Clinton – WhatDoesItMean

August 22, 2016 By: Sorcha Faal, and as reported to her Western Subscribers

The ongoing Security Council (SC) “war” between Alexander Bortnikov, Director of the Federal Security Service (FSB), and Valentina Matviyenko, Chairwoman of the Council of Federation, regarding Hillary Clinton’s secret emails reached a new and toxic level earlier today after President Putin was reported to have “gone ballistic/erupted” upon his being told that the Foreign Intelligence Service (SVR) had, to date, paid to this American presidential candidate upwards of $85 million—with another $200 million expected to be paid out to her by the end of 2017.  [Note:Some words and/or phrases appearing in quotes are English language approximations of Russian words/phrases having no exact counterpart.]


According to this report, and as we had previously (6 May) reported on, Director Bortnikov and Chairwoman Matviyenko have been locked in a bitter struggle over how best the Federation can maximize the usage of Hillary Clinton’s secret emails and telephone calls currently in the possession of SVR—with Bortnikov favoring using them for “persuasion/blackmail” as is currently being done, and Matviyenko advocating their being released to destroy what she considers the “most dangerous American woman in history”.

Continue reading Putin “Erupts” Over Million Dollar “Spy Payments” To Hillary Clinton – WhatDoesItMean →

HILARION 2016 – The Rainbow Scribe

Messages from the Ascended Light Realms

August 21-28, 2016

Beloved Ones,

You are all in the midst of ingesting yet another frequency shift. It is now occurring. There is much that is still being cleansed from your systems. You must remember, Dear Ones, that there are layers upon layers that have been encapsulated, so to speak, which require a slow, safe and gentle cleansing in order to keep you still functioning without succumbing to the chaotic energies that abound in this world or seemingly so. There is much that will be coming forth in the coming months that will make each person on the planet, that will make the minds and hearts of the people of the planet reel, trying to absorb all that is being given to them, that is being mirrored to them in the external world.

It will be a time when all the people of the world will feel fragmented and unable to deal with all the changes that are taking place but ultimately all will come together in a new way, a new beginning that will truly honor each soul upon the planet. Each of you have been prepared for these times, each of you has the training, the knowledge and the ability to be of great use in keeping stability as a primary focus. It behooves you to realize that this is the function that is required during these times, that you keep a level head and try to see the higher perspective of all that is happening and maintain stability, maintain the Light.

Continue reading HILARION 2016 – The Rainbow Scribe →

DR WILLIAM MOUNT: The World Is Waking Up

Sunday, August 21, 2016

Video: The World Is Waking Up – YouTube

The world is apparently waking up and those on top are not liking where we are headed.

Changes – huge changes – are coming as those in charge realize their lives are on the line……Congress, most CIA Members, FBI agents, etc – one false move and this planet becomes a Meteor Shower.

Here are some very interesting stories:

1) While Hillary, and her 3 doubles, are in for Brain Surgery the killings of those who oppose her are continuing.

2) A Bombing it Turkey by a 12 year old child just killed, and wounded, over 59 people. All indication are that the child was armed by ISIS – A Private Hit Agency run out of the US Embassy in Ankara.

Continue reading DR WILLIAM MOUNT: The World Is Waking Up →

HILLARY AND OBAMA CREATED ISIS IN 2012 – NESARANEWS

Saturday, August 20, 2016 by Bethany Blankley

Thanks to Judicial Watch and WikiLeaks, more information continues to come out proving the involvement of Barack Obama and Hillary Clinton in creating and funding the terrorist organization, ISIS.

Several pages of a 2012 report were released, which reveal communication among Barack Obama, Hillary Clinton, the Department of Defense, Homeland Security, and the Department of State’s involvement with over throwing Assad’s Syrian regime, funding al-Qaeda, and the likelihood of ISIS emerging as a prominent force in the Middle East region.

Continue reading HILLARY AND OBAMA CREATED ISIS IN 2012 – NESARANEWS →

Former Navy Officer Exposes TOP Secret Government Pact With Aliens – UFOholic.com

Published on October 9, 2015 by

Willingly or not, some people get to know the dark side of the world, mostly involving Governmental agencies or secret agencies. Most of the time they are dragged along, as the idea of power and secret information as well as being part of top organizations full of “influential” people can easily steal someone’s mind and soul.

Fortunately for us, not all individuals are the same. Some seek redemption after a life of sins, others lose their minds or even commit suicide but, there is also the case when an individual is stronger than the rest and he seeks to enlighten the rest of us, divulging secret information he had access to.

In a situation such as this, they are either considered delirious or absurd or they are assassinated (sooner or later).

Continue reading Former Navy Officer Exposes TOP Secret Government Pact With Aliens – UFOholic.com →

Steve Quayle CERN Giant Reptilian Man Eating Demons in a City Near You | Blogging/Citizen Journalism

Saturday, August 20, 2016 14:26

This is certainly not an easy subject to research. There is tons of information out there, and because of its importance, there is also a lot of disinformation.

I have gone through the sources I found coherent and in tune with my own feeling on the subject, and I’ve done my best to write a version which makes the most sense to me, and perhaps to the reader as well.

When we are researching the old Galactic wars and conflicts between species we need to try to figure out the agenda of the source.

Continue reading Steve Quayle CERN Giant Reptilian Man Eating Demons in a City Near You | Blogging/Citizen Journalism →

19th August 2016. Mike Quinsey.

 
Mike Quinsey Message, August 19, 2016                                                    
19th August 2016. Mike Quinsey.

You who have your ears to the ground will know that “Revaluation” is so near, and together with other changes are soon to signal their commencement. A mammoth task is nearing completion and will give you undeniable proof that the Illuminati have lost their ability to dictate events according to their wishes. They will still exist as a nuisance until they are imprisoned which shall be their ultimate fate. As proof of it, moves that have been waiting for the right time can now go ahead. The negative forces delight in the publicity their actions bring about, but by no means have had things their own way. The Forces of Light continually work behind the scenes preferring to keep their intentions as secret as possible. The truth is that they are superior to the negative ones in all respects, and are able to ensure that matters do not get out of hand. They allow them to develop as planned and do not interfere with karma or the dictates of the higher Forces of Light. Be assured that whatever happens in the course of your experiences is controlled to ensure that the end times work out as planned.

To those souls who are unaware of the greater picture it would seem that everything is chaotic, yet all is in the control of those who ensure that the Plan for Man is followed. Bear in mind that all of you willingly volunteered to experience separation, and accepted the challenge to find your way back to the Light. As individuals and the Human Race, you have been guided ever since the cycle began and even when you ascend there are always Higher Beings who guide your experiences. Through them you grow stronger and able to keep your composure when confronted by the dark Ones. As long as you are strong minded, whatever goes on around you should not affect your ability to remain calm in all circumstances. The lessons learnt are remembered and carried forward from one life to another.

Continue reading 19th August 2016. Mike Quinsey. →

“Planetary Shift IN, nwo OUT”, 2 of 2… Russia/Iran/China: Changing things in the Middle East (or, “It’s time to slap New World Order agents in their faces”) | Kauilapele’s Blog

Please note that “nwo” is not capitalized, as most articles do, since, in my view, they are “on the outs”, and do not rate any capitalizations.

Three articles are summarized here, the first from Lada Ray, the next two from VT’s Jim Dean and Jonas Alexis.

Title and link with a few highlights from each.

THE SHIFT: China in Syria; Iran Hosts Russia at Hamadan Base; Iraq Opens Skies to Russian Bombers (Futurist Trendcast, 8-15-16)

Continue reading “Planetary Shift IN, nwo OUT”, 2 of 2… Russia/Iran/China: Changing things in the Middle East (or, “It’s time to slap New World Order agents in their faces”) | Kauilapele’s Blog →

“Planetary Shift IN, nwo OUT”, 1 of 2… Turkey: “Explosive Consequences of Putin-Erdogan St.Petersburg Meeting” (FT) and “Turkey considering military ties with Russia” (VT) | Kauilapele’s Blog

Posted on by

Please note that “nwo” is not capitalized, as most articles do, since, in my view, they are “on the outs”, and do not rate any capitalizations.

One of these (the Lada Ray) was posted here yesterday. The other is from VT (posted 8-18-16). It basically shows Turkey as “giving the (possibly middle) finger” to NATO-USA CORP. So in my view, it’s a great sign of MAJOR planetary change.

I’m adding a few highlights from each along with the title and link.

Explosive Consequences of Putin-Erdogan St.Petersburg Meeting and Earth Shifting Changes it Foretells! (Futurist Trendcast, 8-15-16)

Continue reading “Planetary Shift IN, nwo OUT”, 1 of 2… Turkey: “Explosive Consequences of Putin-Erdogan St.Petersburg Meeting” (FT) and “Turkey considering military ties with Russia” (VT) | Kauilapele’s Blog →

NSA Hacked by unknown hackers called ‘The Shadow Brokers’ | Stillness in the Storm

August 16th 2016 by Aaron Kesel

The Equation Group, a cyber-attack group allegedly associated with the U.S. National Security Administration (NSA), has been hacked in an unconfirmed data dump of exploits and secret tools according to TheHackerNews.

An unknown hacker or a group of hackers calling themselves The Shadow Brokers, in addition to offering free hacked tools online, also auctioned hacked tools for $568 Million dollars in Bitcoin.

Equation Group was linked to the previous infamous Regin and Stuxnet cyber attacks now known to be state sponsored malware attacks.

Continue reading NSA Hacked by unknown hackers called ‘The Shadow Brokers’ | Stillness in the Storm →

HUGE VICTORY! Federal Court Bans Govt from Prosecuting Medical Pot Users and Growers | Stillness in the Storm

August 17th 2016 by Matt Agorist

Last week, the tyrannical DEA doubled down on their asinine and immoral decision to classify marijuana as having no medical value — promising to continue to kidnap, cage, and kill people for possessing it. However, in a major victory, and a well-deserved slap to the face of the DEA, a federal appeals court just ruled that prosecuting medical marijuana users and growers is now banned.

The Ninth US Circuit Court of Appeals’ three-judge panel has ruled that the Department of Justice (DOJ) cannot spend budget money to prosecute people who grow, sell or use medical marijuana—if they comply with state law.

The 25 states who’ve found themselves subject to continuous raids — in spite of medical pot being legal — will now have solace in the fact that the DOJ can no longer throw money at the futile and immoral practice of arresting people for a plant.

Continue reading HUGE VICTORY! Federal Court Bans Govt from Prosecuting Medical Pot Users and Growers | Stillness in the Storm →

George Soros Paid Al Gore Millions To Lie About Global Warming | Your News Wire

August 19, 2016 by Sean Adl-Tabatabai

Newly leaked documents reveal that billionaire George Soros bribed former Vice President Al Gore with millions of dollars in order to fabricate data about global warming. 

According to a document published by DC Leaks, Soros used his Open Society Institute to pay Al Gore $10 million dollars per year in order to make Gore exaggerate claims about man-made climate change to the public.

Dailycaller.com reports:

“U.S. Programs Global Warming Grants U.S. Programs became engaged on the global warming issue about four years ago, at George Soros’s suggestion,” reads a leaked OSI memo.

Continue reading George Soros Paid Al Gore Millions To Lie About Global Warming | Your News Wire →

THE QUEEN’S ARREST IS IMMINENT. | Matt Taylor – Brighton

January 31, 2014

The Queen’s face etched with fear, following paedophile arrest warrant, ordered by former Royal Military Policeman, Matt Taylor.

The Queen has granted herself (and her family) a new right of absolute secrecy unsurpassed in British history, in an attempt to cover up paedophile claims and arrest warrants.

Royal Family granted new right of Absolute secrecy.

Looking visibly shaken and exhausted after the relentless attack on her crown, the Queen has taken this last ditched attempt to silence the paedophile rumours in connection with the Yewtree police investigation and her Jimmy Savile connections.

Continue reading THE QUEEN’S ARREST IS IMMINENT. | Matt Taylor – Brighton →

Russia and The Khazars | Veterans Today

[Editor’s Note: When you look at the biography of congressional representatives or U.S. senators who are dual Israeli citizens, or media moguls, or titans of the film industry, for example, you will often notice that the parents, or grandparents, or even the great grandparents are mentioned as Jewish immigrants from Russia or the Ukraine or other eastern European countries, including Turkey. These are the descendants of the Khazarian Jews discussed in this article.

This article, published in 1951 would never be allowed to reach print today, it would be decried as ‘anti-semitic’ and have groups like the ADL and AIPAC actively opposing and supressing it.

That is because it is a true and accurate retelling of how the Khazars became Jews and rose to such power by infiltrating the US. Essential reading, especially for our US brethen.

Ian]

Russia and The Khazars

By John Beaty

First published in 1951

Chapter 2 from The Iron Curtain Over America

The Zionists who have overtaken America are principally of Russian Khazar origin

Having traced the Knighthood of the Teutonic Order from its origin to its dissolution as a military-religious brotherhood, and having noted the development of successor sovereignties down to the obliteration of Prussia in 1945, we must turn back more than a thousand years, to examine another thread — a scarlet one — in the tangled skein of European history.

Continue reading Russia and The Khazars | Veterans Today →

Office of Poofness 8-17-16… “Mid-week Report” (plus, request for help) | Kauilapele’s Blog

Here is Zap’s mid-week update. He also posted a special request for help for dental abscess surgery and other needs of his team. I’ve placed that message below the mid-week message.

” WE ARE ALMOST THERE. WE HAVE BEEN ALMOST THERE FOR YEARS, BUT THIS TIME THE SYSTEM HAS CLEANED UP ENOUGH TO GET THE FIRST FUNDS RELEASED WITHIN THIS MONTH. THE ARRESTS AND OTHER CLEANUP HAS RESULTED, FOR EXAMPLE, IN THE CLOSING OF THE MAJOR ACCOUNTS WITHIN HSBC HK FOR ALMOST A FULL DAY AS THEY DID THE INTERNAL CLEANUP.

“WE HAVE FINAL APPROVAL FROM THE REGULATORS FOR OUR FUNDS, AND WITH LUCK THEY WILL BE HERE REALLY REALLY SOON, BUT RIGHT NOW WE ARE PLACED ON A BIT OF A BLACKOUT UNTIL ALL OF THAT IS COMPLETED.

“EVERYTHING ELSE IS MOVING FORWARD QUICKLY NOW. THE COMMITTEE THAT IS DOING THE RV HAS STARTED THE PAYMENTS FOR THE BIG STUFF, AND IT LOOKS LIKE THE SMALL/PUBLIC STUFF WILL KICK IN ANY MOMENT AS WELL. THE HISTORIC BOND STUFF UNDER THE TRUST IS ALSO MOVING, AND THEY WILL BEGIN WITH THE BONDS ANYTIME AS WELL.

“MAJOR MONEY MOVEMENTS ARE OCCURRING AND THIS IS A CLEAR SIGNAL AS TO THE GLOBAL STATE OF PREPAREDNESS FOR WHAT IS TO COME. ALL IN ALL, IT IS PRETTY GOOD AND WE ARE IN GREAT SHAPE FOR THE FUTURE.”

Kp note: I always take these “Poofnesses” as potential data. Bottom line, how does it hit my Higher Innards”? Does it “ring” true within (if it “rings” at all)?

Office of Poofness support links are at the end of each posting. To support RMN for publishing these each week, please click here.

——————————————————–

HI ALL

WE ARE ALMOST THERE. WE HAVE BEEN ALMOST THERE FOR YEARS, BUT THIS TIME THE SYSTEM HAS CLEANED UP ENOUGH TO GET THE FIRST FUNDS RELEASED WITHIN THIS MONTH.

THE ARRESTS AND OTHER CLEANUP HAS RESULTED, FOR EXAMPLE, IN THE CLOSING OF THE MAJOR ACCOUNTS WITHIN HSBC HK FOR ALMOST A FULL DAY AS THEY DID THE INTERNAL CLEANUP. I DO NOT KNOW THE DETAILS, BUT WHEN THEY CAME BACK UP AND RUNNING, CHANGES WERE NOTICED AND THOSE SPOKE TO THE REVAMP.

THE EXECUTIVE THAT PROVED TO BE A GOOD THIEF IS UNDER THE WATCHFUL EYE OF THE GOVERNMENT GUYS. IN HIS HOME. UNDER HOUSE ARREST OF SORTS. HE HAS TO FINISH WHAT HE WAS CHARGED WITH OR ELSE.

Continue reading Office of Poofness 8-17-16… “Mid-week Report” (plus, request for help) | Kauilapele’s Blog →

It Is Happening: US to Hand Over Control of the Internet as of October 1

The United States will fulfill a years-old promise to privatize the governance of the World Wide Web in October.

The Internet Corporation for Assigned Names and Numbers (ICANN) was established in 1988 to coordinate domain names across the globe. A nonprofit organization, ICANN is overseen by the US Department of Commerce.

Naturally, a number of countries and privacy advocates have expressed concern that a global entity as vital as the internet is under the control of the US, and the Obama Administration promised to cede control over ICANN.

Until recently, Washington had failed to make good on this promise. But on Tuesday, Assistant Secretary Lawrence Strickling confirmed that the process will be finalized in roughly two months.

Continue reading It Is Happening: US to Hand Over Control of the Internet as of October 1 →

DR WILLIAM MOUNT: Hillary’s Phone Calls Hacked

Wednesday, August 17, 2016

HILLARY ONE RINGY DINGY, PHONE CALLS HACKED

Video:…Hillary, One Ringy Dingy, Her Phone Calls Released – YouTube

This is correct. All of Hillary’s phone calls are being released.

What a News Day – so follow along closely and prepare to be wowed:

AA) Emails Released

The Emails of the following were released

1) Hillary
2) Traitor John McCain
3) George Soros
4) NSA
5) Obama’s Emails are about to be released as his Facebook and Twitter Accounts were just hacked.

This means the details of every Hillary weapons sale, from the First Gulf War in Iraq to the last war in Syria – it is all being exposed.

Continue reading DR WILLIAM MOUNT: Hillary’s Phone Calls Hacked →

Panic Grips America, Shuts Down NSA, After Russia “Reveals” It Has All Hillary Clinton Phone Calls – WhatDoesItMean

sorka faal

August 17, 2016 By: Sorcha Faal, and as reported to her Western Subscribers

A series of astounding, and often contradictory, reports emanating from the Security Council (SC), and circulating throughout the Kremlin today, show that a chasm has been created among many ministries (especially within the military and intelligence communities) due to President Putin’s “order/decree” to let the Obama regime know that the Federation was not only in control of all of Hillary Clinton’s “missing/disappeared” emails, but also of all her telephonic communications too. [Note: Some words and/or phrases appearing in quotes are English language approximations of Russian words/phrases having no exact counterpart.]


Continue reading Panic Grips America, Shuts Down NSA, After Russia “Reveals” It Has All Hillary Clinton Phone Calls – WhatDoesItMean →

Catholic Battle for the White House | SOTN: Alternative News & Commentary

Will Kaine Slay Abel Again?

The Jesuits have put their man in place, and he stands only one heartbeat or resignation away from the White House should Hillary Clinton win. Once he is in place, the Jesuits will control the World Triumvirate—the City of London, the Vatican, and Washington, D.C.  Patriots, this is the ultimate fight we must face because once the Jesuits are in control, they will have won their age-old battle—WORLD DOMINATION—with us as its financial, political, and religious slaves.

In this article you will learn:

  • How Patriots made the White and Black Popes re-strategize their world domination plans
  • The unique position Tim Kaine has with the Jesuits
  • The Clinton connection to the Knights of Malta
  • Pope Francis moves from Rome to Astana, Kazakhstan
  • Two globalist groups vying for the Vatican and the White House

As always, we offer this insight from our Anonymous Patriots Think Tank so that you can disseminate this important information to your constituency in a manner that resonates with them. We firmly believe that the New Fourth Estate—which is independent news and investigative journalism from folks like you and us—continue to give the Cabal upsets as we become aware of their hidden agendas. They had no idea Patriots are so “awake” in our critical thinking and have such a prolific underground network activated.

Continue reading Catholic Battle for the White House | SOTN: Alternative News & Commentary →

‘Pleading The Hillary’: Assange Demands Same Treatment From DOJ | Your News Wire

August 16, 2016 by Baxter Dmitry

Julian Assange says the Department of Justice (DoJ) investigation of Hillary Clinton “set a new standard” and the WikiLeaks founder is now demanding the precedents set by the DoJ should be applied to their never ending case against him.

Assange appeared on CNN’s The Lead on Monday via video link from the Ecuadorian embassy in London where he has been exiled since 2012.

“Our D.C. lawyers are delivering a letter tomorrow to Attorney General Loretta Lynch asking her to explain why it is that the now six-year-long national security and criminal investigation being run against WikiLeaks, the reason I have political asylum, has not been closed,” he said.

Continue reading ‘Pleading The Hillary’: Assange Demands Same Treatment From DOJ | Your News Wire →